Workflow Automation · BraivIQ AI Engineering Playbook
AI Deployment Secrets: Keeping Registry Tokens Out Of CI Logs After The LangGraph CLI Advisory
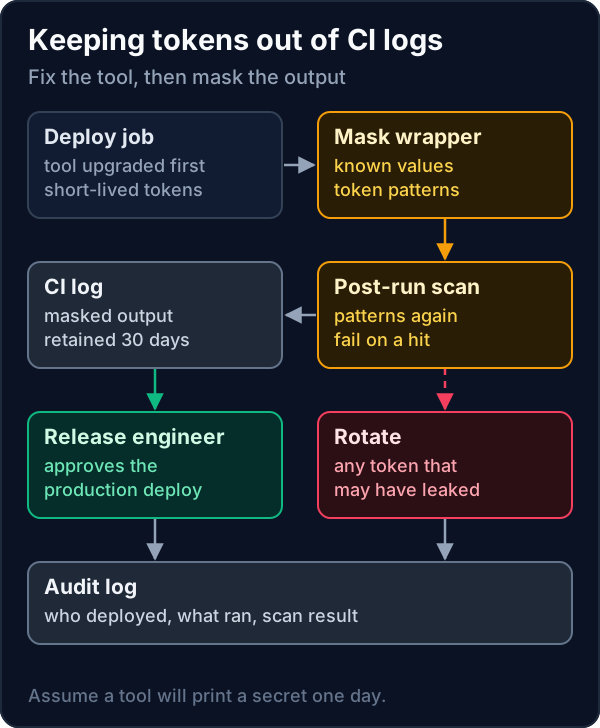
AI deployment secrets leak most often through logs, not code. On 28 October 2026 an advisory for langgraph-cli, CVE-2026-115885 fixed in 0.4.32, explained that langgraph deploy --verbose printed the temporary registry push token, so anyone who could read the CI log could use it until it expired. Upgrade first. Then add a second layer for every tool in the pipeline: a wrapper that masks known secret values and token patterns before any line reaches the log, a scan after the run, rotation when in doubt and a named engineer approving production deploys.
Published · Updated · 8 min read · By BraivIQ Engineering
Key takeaways
- langgraph-cli 0.4.15 to 0.4.31 printed the temporary registry push token with deploy --verbose (CVE-2026-115885, CVSS 5.4, published 28 October 2026). 0.4.32 fixes it.
- Anyone who could read the CI output could use the token until it expired, according to the advisory.
- Wrap deploy commands so known secret values and common token patterns are masked before output reaches the log.
- Scan logs after each run, rotate any token that may have leaked, and keep a named approver on production deploys.
AI deployment secrets are the API keys, registry tokens and signing keys a pipeline needs to ship an agent. The usual leak is a verbose flag, a debug print or a stack trace in CI output. Fix the tool that leaks, then assume another will, and mask output before it is stored.
What did the langgraph-cli advisory say?
The advisory published on 28 October 2026 (CVE-2026-115885, CVSS 5.4) says that langgraph deploy --verbose printed the temporary registry push token the CLI uses to log Docker in to the deployment's image registry. Anyone who could read that output, for example in CI logs, could use the token until it expired. Versions 0.4.15 to 0.4.31 are affected and 0.4.32 fixes it.
How do you keep AI deployment secrets out of CI output?
ci_redact.py"""Run a deploy command in CI and mask secrets before anything reaches the log.
CVE-2026-115885 (langgraph-cli 0.4.15 to 0.4.31, fixed in 0.4.32, 28 October 2026): `langgraph deploy
--verbose` printed the temporary registry push token, so anyone who could read CI logs could reuse it.
Upgrade first. This wrapper is a second layer for any tool. Python 3.14 standard library only.
"""
from __future__ import annotations
import os
import re
import subprocess
import sys
PATTERNS = [re.compile(p) for p in (r"(?i)(token|password|secret|api[_-]?key)(\s*[:=]\s*)(\S+)",
r"\bsk-[A-Za-z0-9_-]{16,}\b", r"\beyJ[A-Za-z0-9_-]{10,}\.[A-Za-z0-9_.-]+")]
def mask(line: str, known: list[str]) -> str:
for value in known:
if len(value) >= 8:
line = line.replace(value, "****")
line = PATTERNS[0].sub(lambda m: m.group(1) + m.group(2) + "****", line)
for p in PATTERNS[1:]:
line = p.sub("****", line)
return line
def run(cmd: list[str], secret_env: list[str]) -> int:
known = [os.environ[k] for k in secret_env if os.environ.get(k)]
proc = subprocess.Popen(cmd, stdout=subprocess.PIPE, stderr=subprocess.STDOUT, text=True)
assert proc.stdout is not None
for line in proc.stdout:
sys.stdout.write(mask(line, known))
return proc.wait()
if __name__ == "__main__":
os.environ["REGISTRY_TOKEN"] = "rt_live_5b1f0c9e7a2d4c6b"
fake_deploy = ("print('logging in with token=rt_live_5b1f0c9e7a2d4c6b');"
"print('pushed image, key sk-test_abcdefghijklmnopqrst');print('done')")
code = run([sys.executable, "-c", fake_deploy], secret_env=["REGISTRY_TOKEN"])
print("exit code:", code)Python 3.14.4, standard library only. Run once as shown. The token and key in the demo are fake.
The fake deploy prints a token and an sk- style key. The wrapper replaces the token by its known value from the environment and the key by pattern, and passes the exit code through so the pipeline still fails correctly. Most CI systems also mask registered secrets, so use theirs as well. This wrapper covers tools that print values your CI system does not know about.
What breaks in production?
- **Secrets split across lines.** A token wrapped by a long line can escape a line-by-line mask. Keep tokens short-lived.
- **Artifacts and caches.** Masking the console does not clean files the job uploads. Scan artifacts too.
- **Patterns that miss new formats.** Prefer known values from the environment, with patterns as a backstop.
- **Old logs.** After an advisory like this one, search existing logs for the window when affected versions ran, and rotate.
What are the alternatives to a masking wrapper?
| Option | Good fit | Trade-off |
|---|---|---|
| CI system secret masking | Every pipeline | Only masks values it was given |
| Workload identity instead of tokens | Cloud deployments | No long-lived secret to leak, more setup |
| Wrapper plus post-run scan, as above | Pipelines with many third-party tools | Small code to maintain |
Our playbook on MCP integration hardening covers tokens at run time, and securing your tracking server covers secrets in traces. Our blog on AI agent security gives the vendor questions.
Where should a team start?
Upgrade langgraph-cli if you use it, search CI logs from the affected period for registry logins and rotate anything you find. Then add the wrapper to every deploy step. Our Workflow Automation London team builds pipelines this way, as the services page describes, and the 14-day Proof Run ships with a reviewed pipeline.
Frequently asked questions
Which langgraph-cli version fixes the token leak?
langgraph-cli 0.4.32 fixes CVE-2026-115885. Versions 0.4.15 to 0.4.31 are affected, according to the advisory published on 28 October 2026.
How do you stop secrets appearing in CI logs?
Use your CI system's secret masking, wrap third-party tools so output is masked before it is stored, prefer short-lived tokens or workload identity, and scan logs and artifacts after each run.
What should you do if a token was printed in a CI log?
Rotate it, restrict who can read the affected logs, delete them if your retention policy allows, and check the registry or service for use of the token during the exposure window.
References
- GitHub Advisory Database, "LangGraph CLI prints the registry push token in langgraph deploy --verbose output (CVE-2026-115885)", 28 October 2026. https://github.com/advisories/GHSA-8prr-f582-jqq3